Tridenty Auditor is a GRC platform to implement and audit ISO/IEC 27001:2022 and the CNO Cybersecurity Guide (Agreement 1960): 134 preloaded controls, a guided path that does not advance without approved evidence and documents sealed with a SHA-256 hash and two signatures.
SHA-256 · Two signatures · Guided path · Multi-tenant
WHY TRIDENTY AUDITOR
Complying with an information security standard shouldn't mean chasing evidence across emails and shared folders. Tridenty Auditor centralizes the whole cycle in a single multi-tenant platform. It isn't a flat checklist: it's a path that blocks progress without approved evidence, and every approved document is sealed with a SHA-256 hash and two signatures, verifiable at any time.
The compliance indicator only goes up when there is an approved document behind every control or task. The number you see is the one you can defend in front of an external auditor.
Two signatures (reviewed and approved), a SHA-256 hash per version and a stamped PDF as a controlled copy, marked OBSOLETE or DRAFT when applicable. One click recalculates the hash and confirms nobody touched the file.
ISMS Path (8 phases) or CNO Path (10 phases) with tasks, owners and mandatory evidence. A phase does not unlock until the previous one is closed.
Documents, processes, risks, SoA, legal requirements and audit share the same controls and the same evidence. No more spreadsheets that never add up.
Four roles with segregation of duties (the auditor can't approve their own evidence) on an architecture that isolates each customer's data in the database.
The full Annex A of ISO/IEC 27001:2022 and the 41 controls of CNO Agreement 1960, with their evidence requirements, come preloaded. Nothing to enter by hand before you start.
Seven modules that share the same controls and the same evidence.
Versioning with a draft → review → two-signature approval flow, SHA-256 seal, stamped PDF, "read and understood" acknowledgment, retention with disposition and legal hold, templates and full-text search in Spanish.
ISMS Path or CNO Path according to the tenant's standard: tasks with owner, date and mandatory evidence; unlock by phase. Turns the standard into a work plan.
Assets, probability × impact matrix, treatment plan and residual risk, linked to the controls that mitigate it.
The standard's controls with applicability, exclusion justification and an owner per control. A living SoA, not a PDF that goes out of date.
Audit program, classified findings and CAPA with root cause, owner, % progress and estimated cost; auditor's assessment on closing and evidence-verifiable closure.
Process tree with linked documents and an embedded viewer; landing dashboard with ISMS status and document hygiene.
Matrix of legal, regulatory and contractual requirements with owner, evidence and compliance level (ISO 27001 cl. 4 and A.5.31).
Record of who did what, when and from where; four roles; Spanish-language interface, light and dark mode, and use on desktop, tablet and mobile.
ON SCREEN
Compliance indicator: a single percentage visible across the whole platform that only goes up with approved evidence on the SoA, the Path and the legal matrix. It measures real implementation maturity, not just document validity.
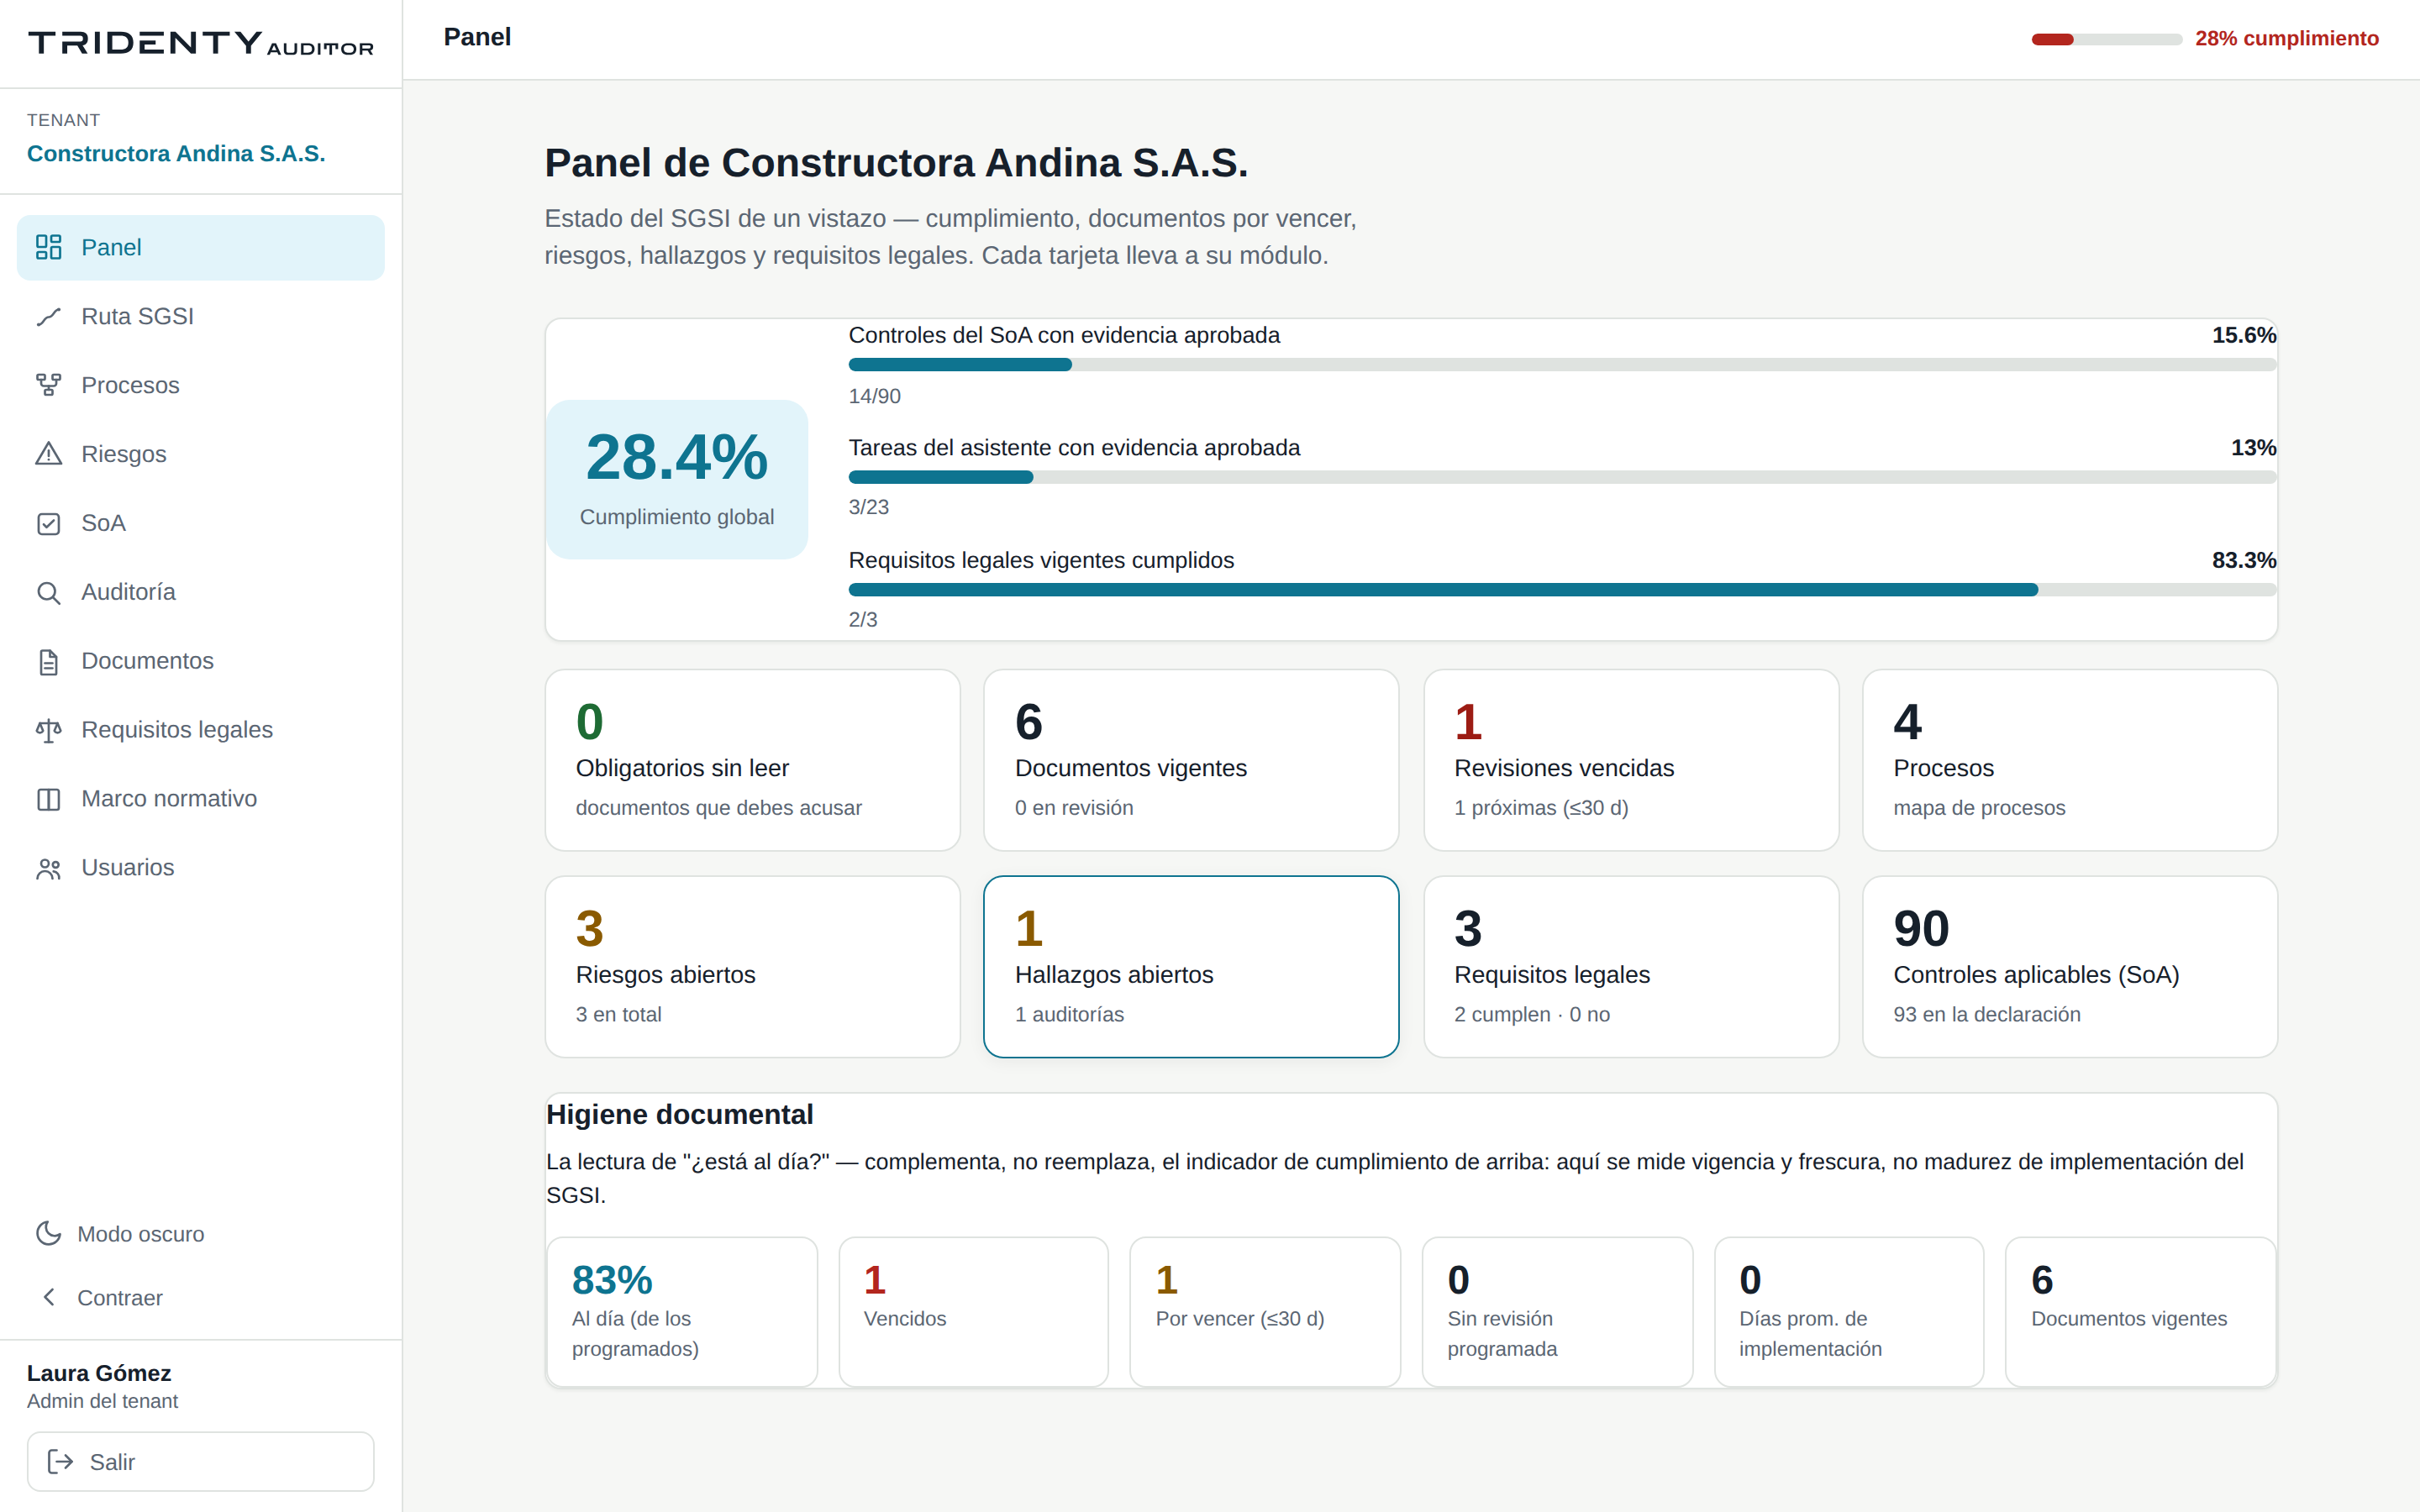
Live compliance indicator, ISMS status and document hygiene: overdue, due soon and implementation days.
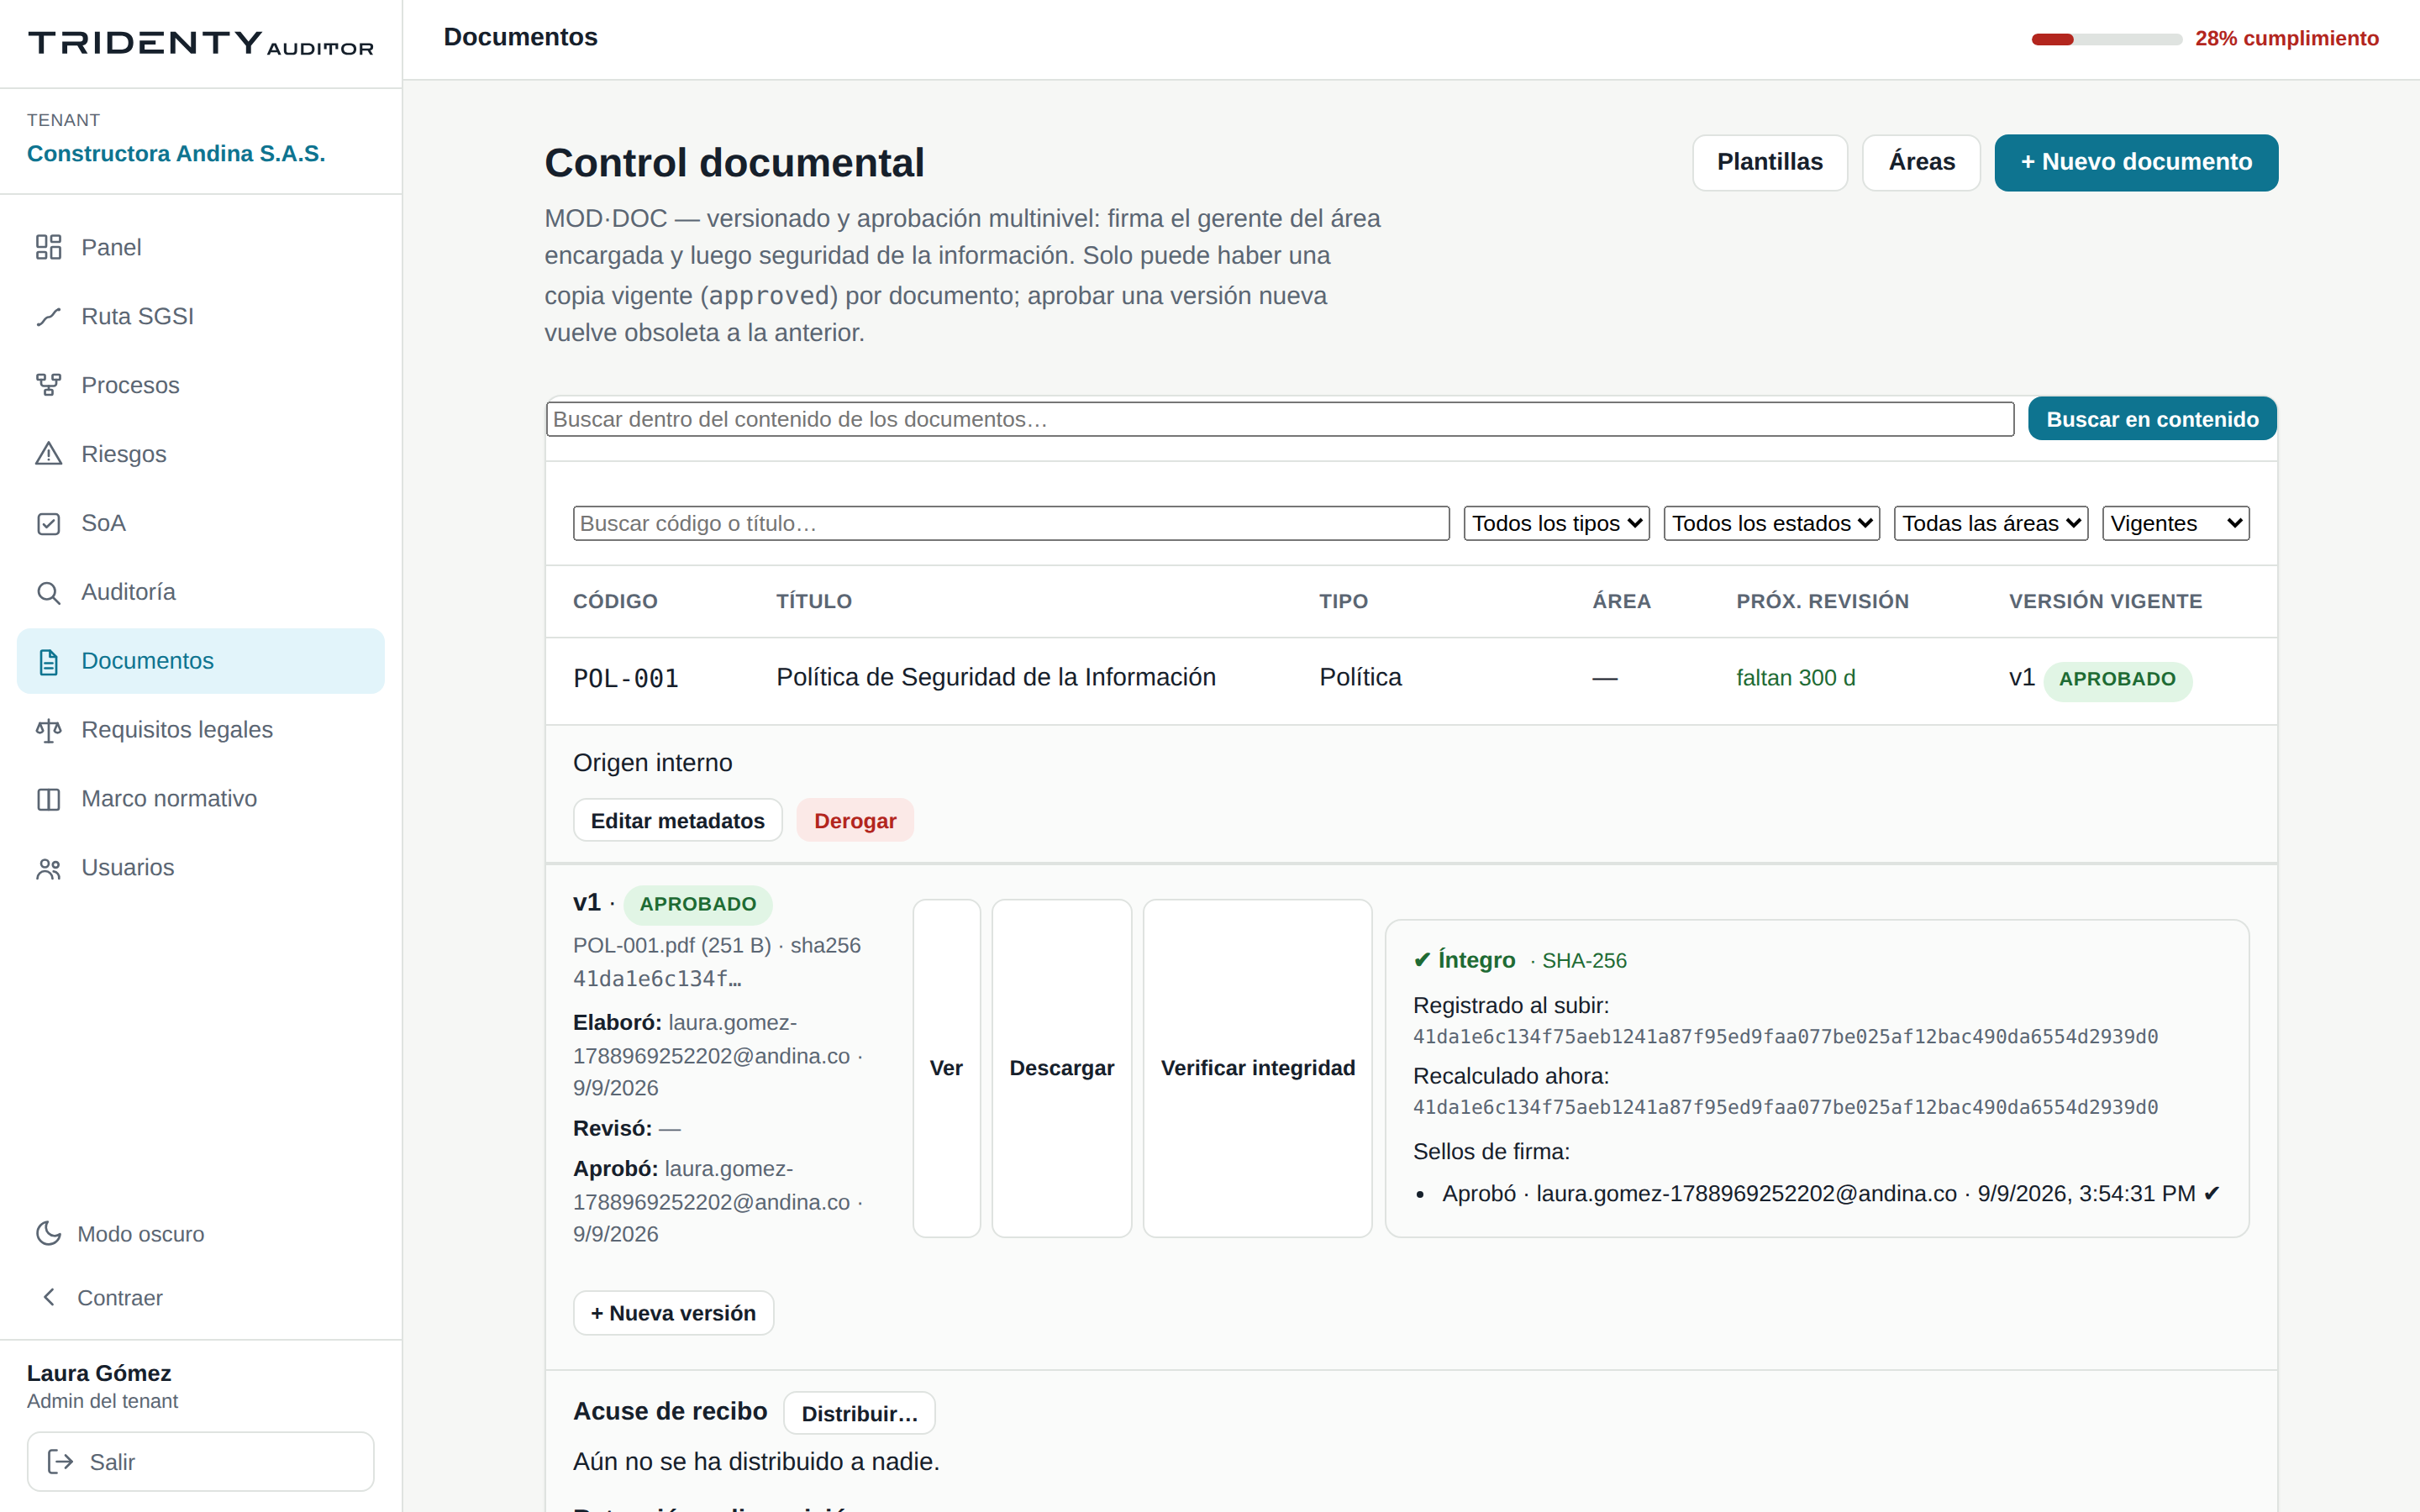
Signatures, seal and SHA-256 integrity verification in one click.
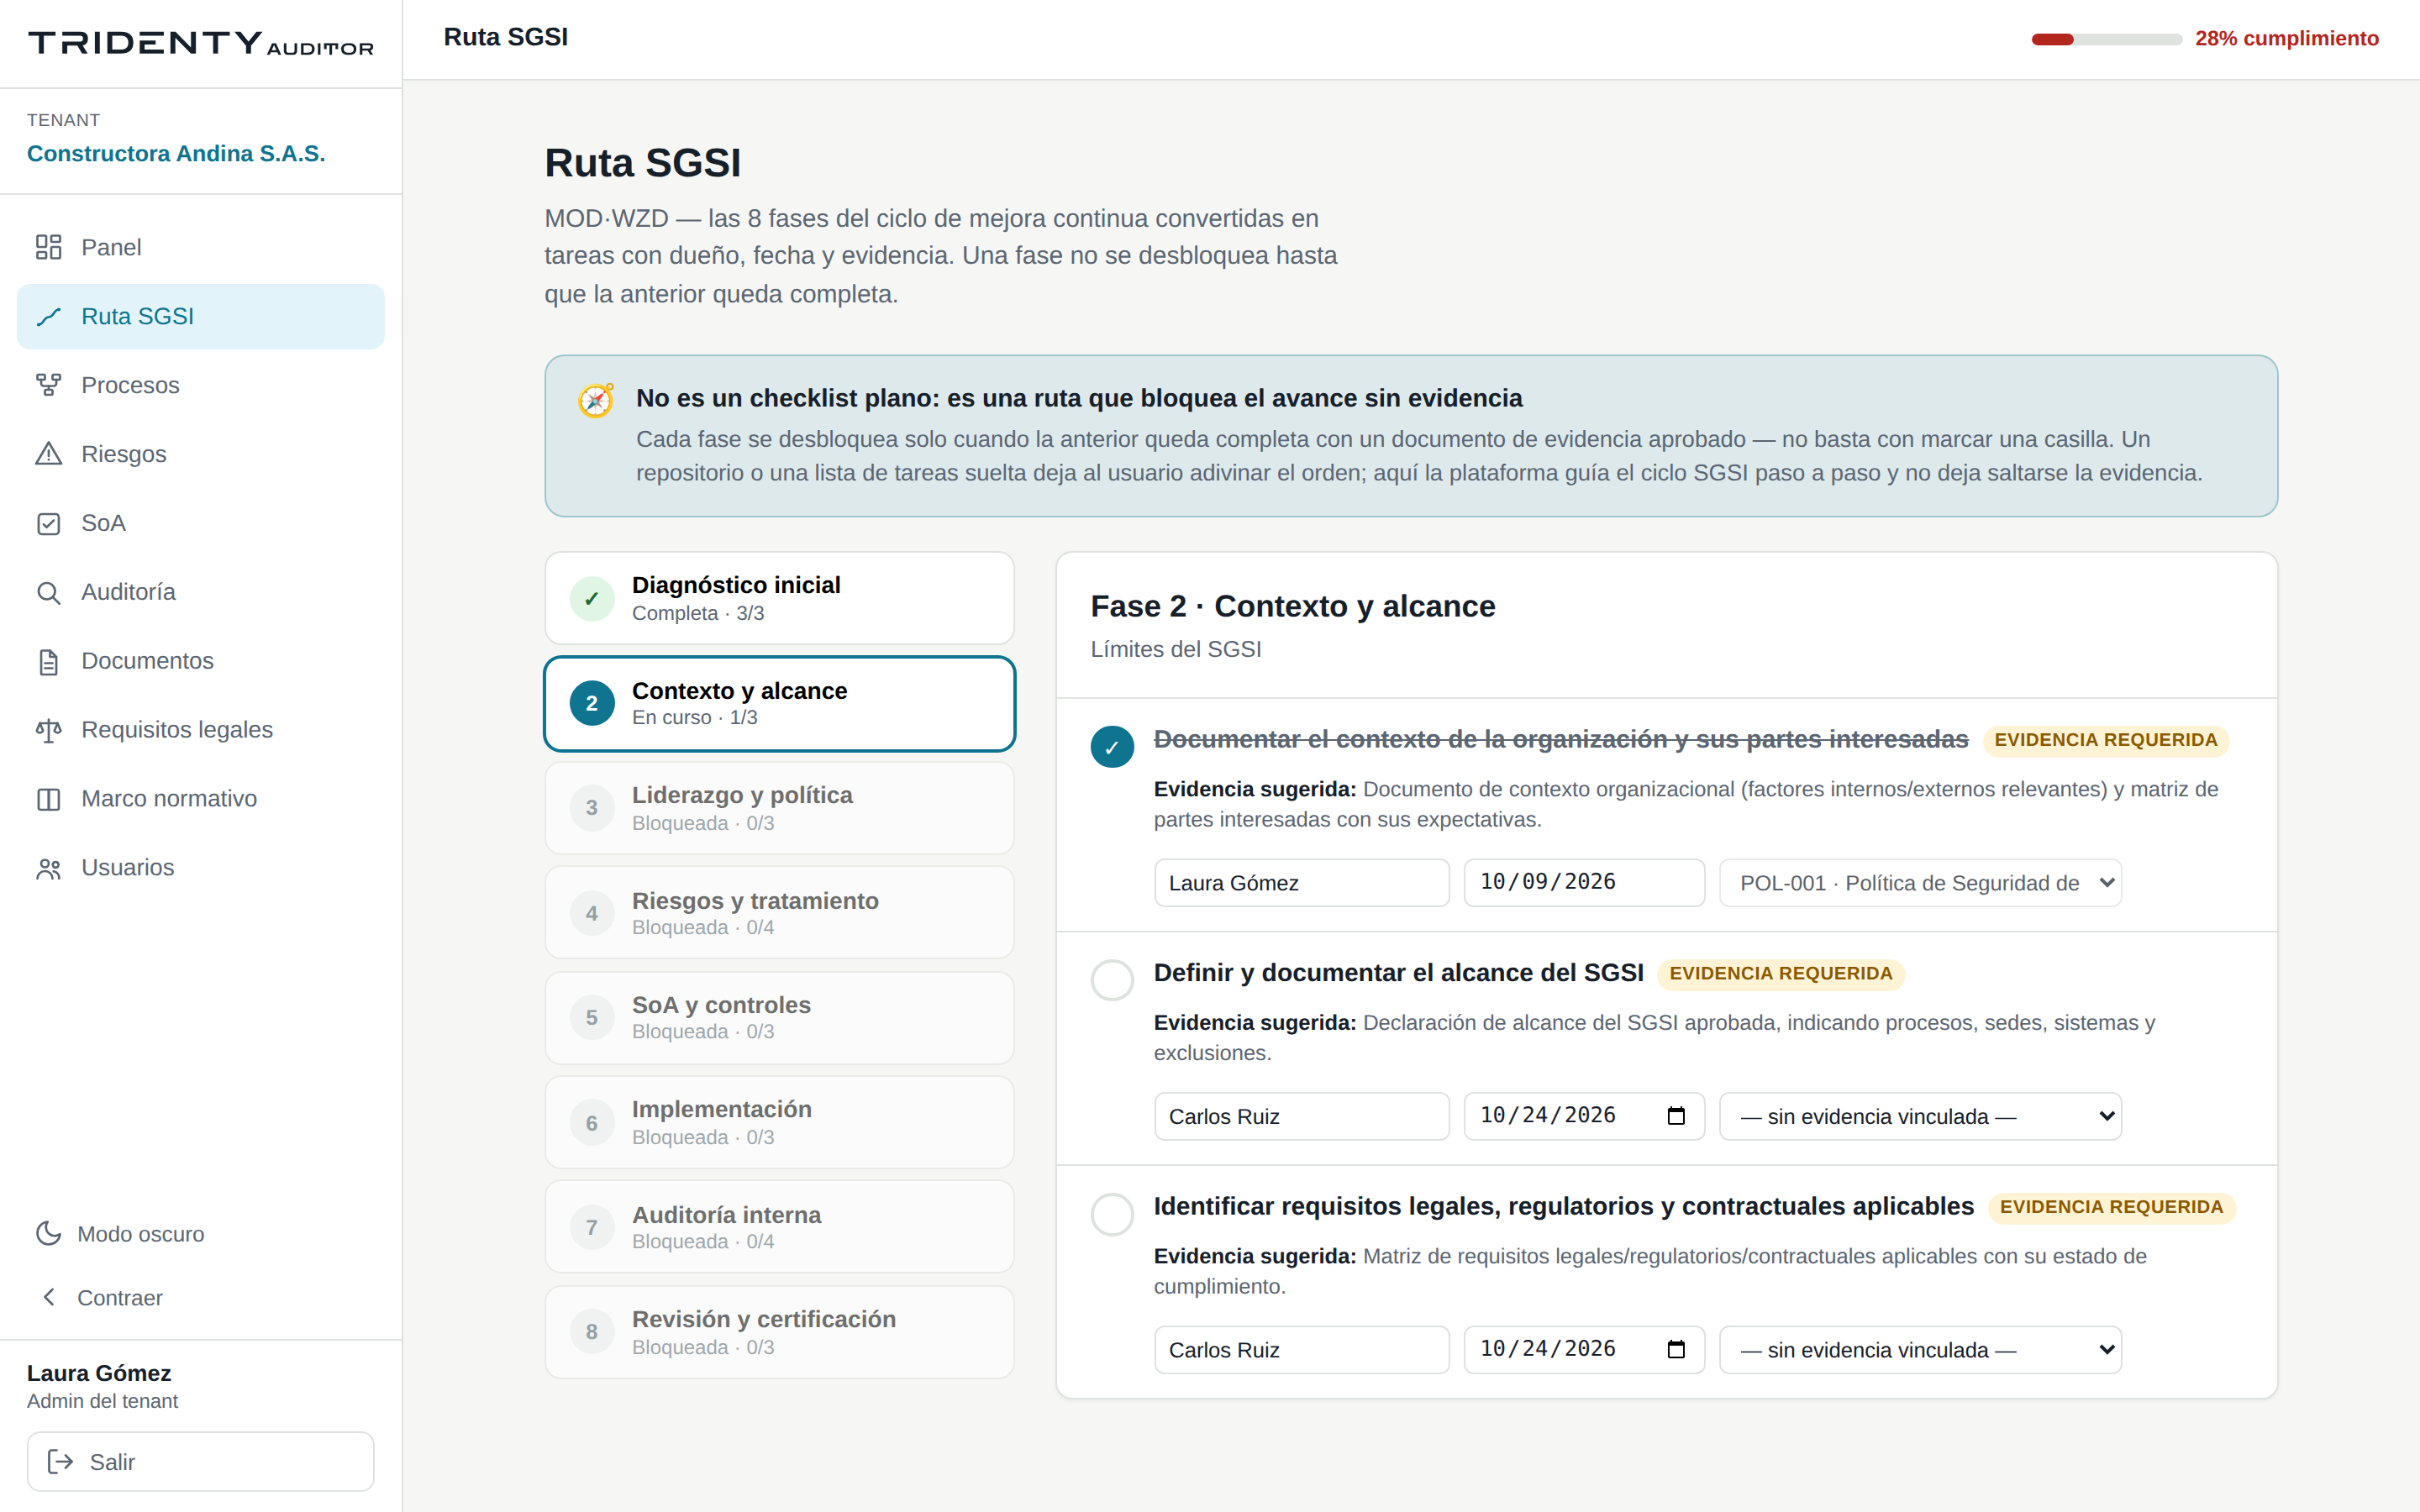
Phases that only unlock with approved evidence.
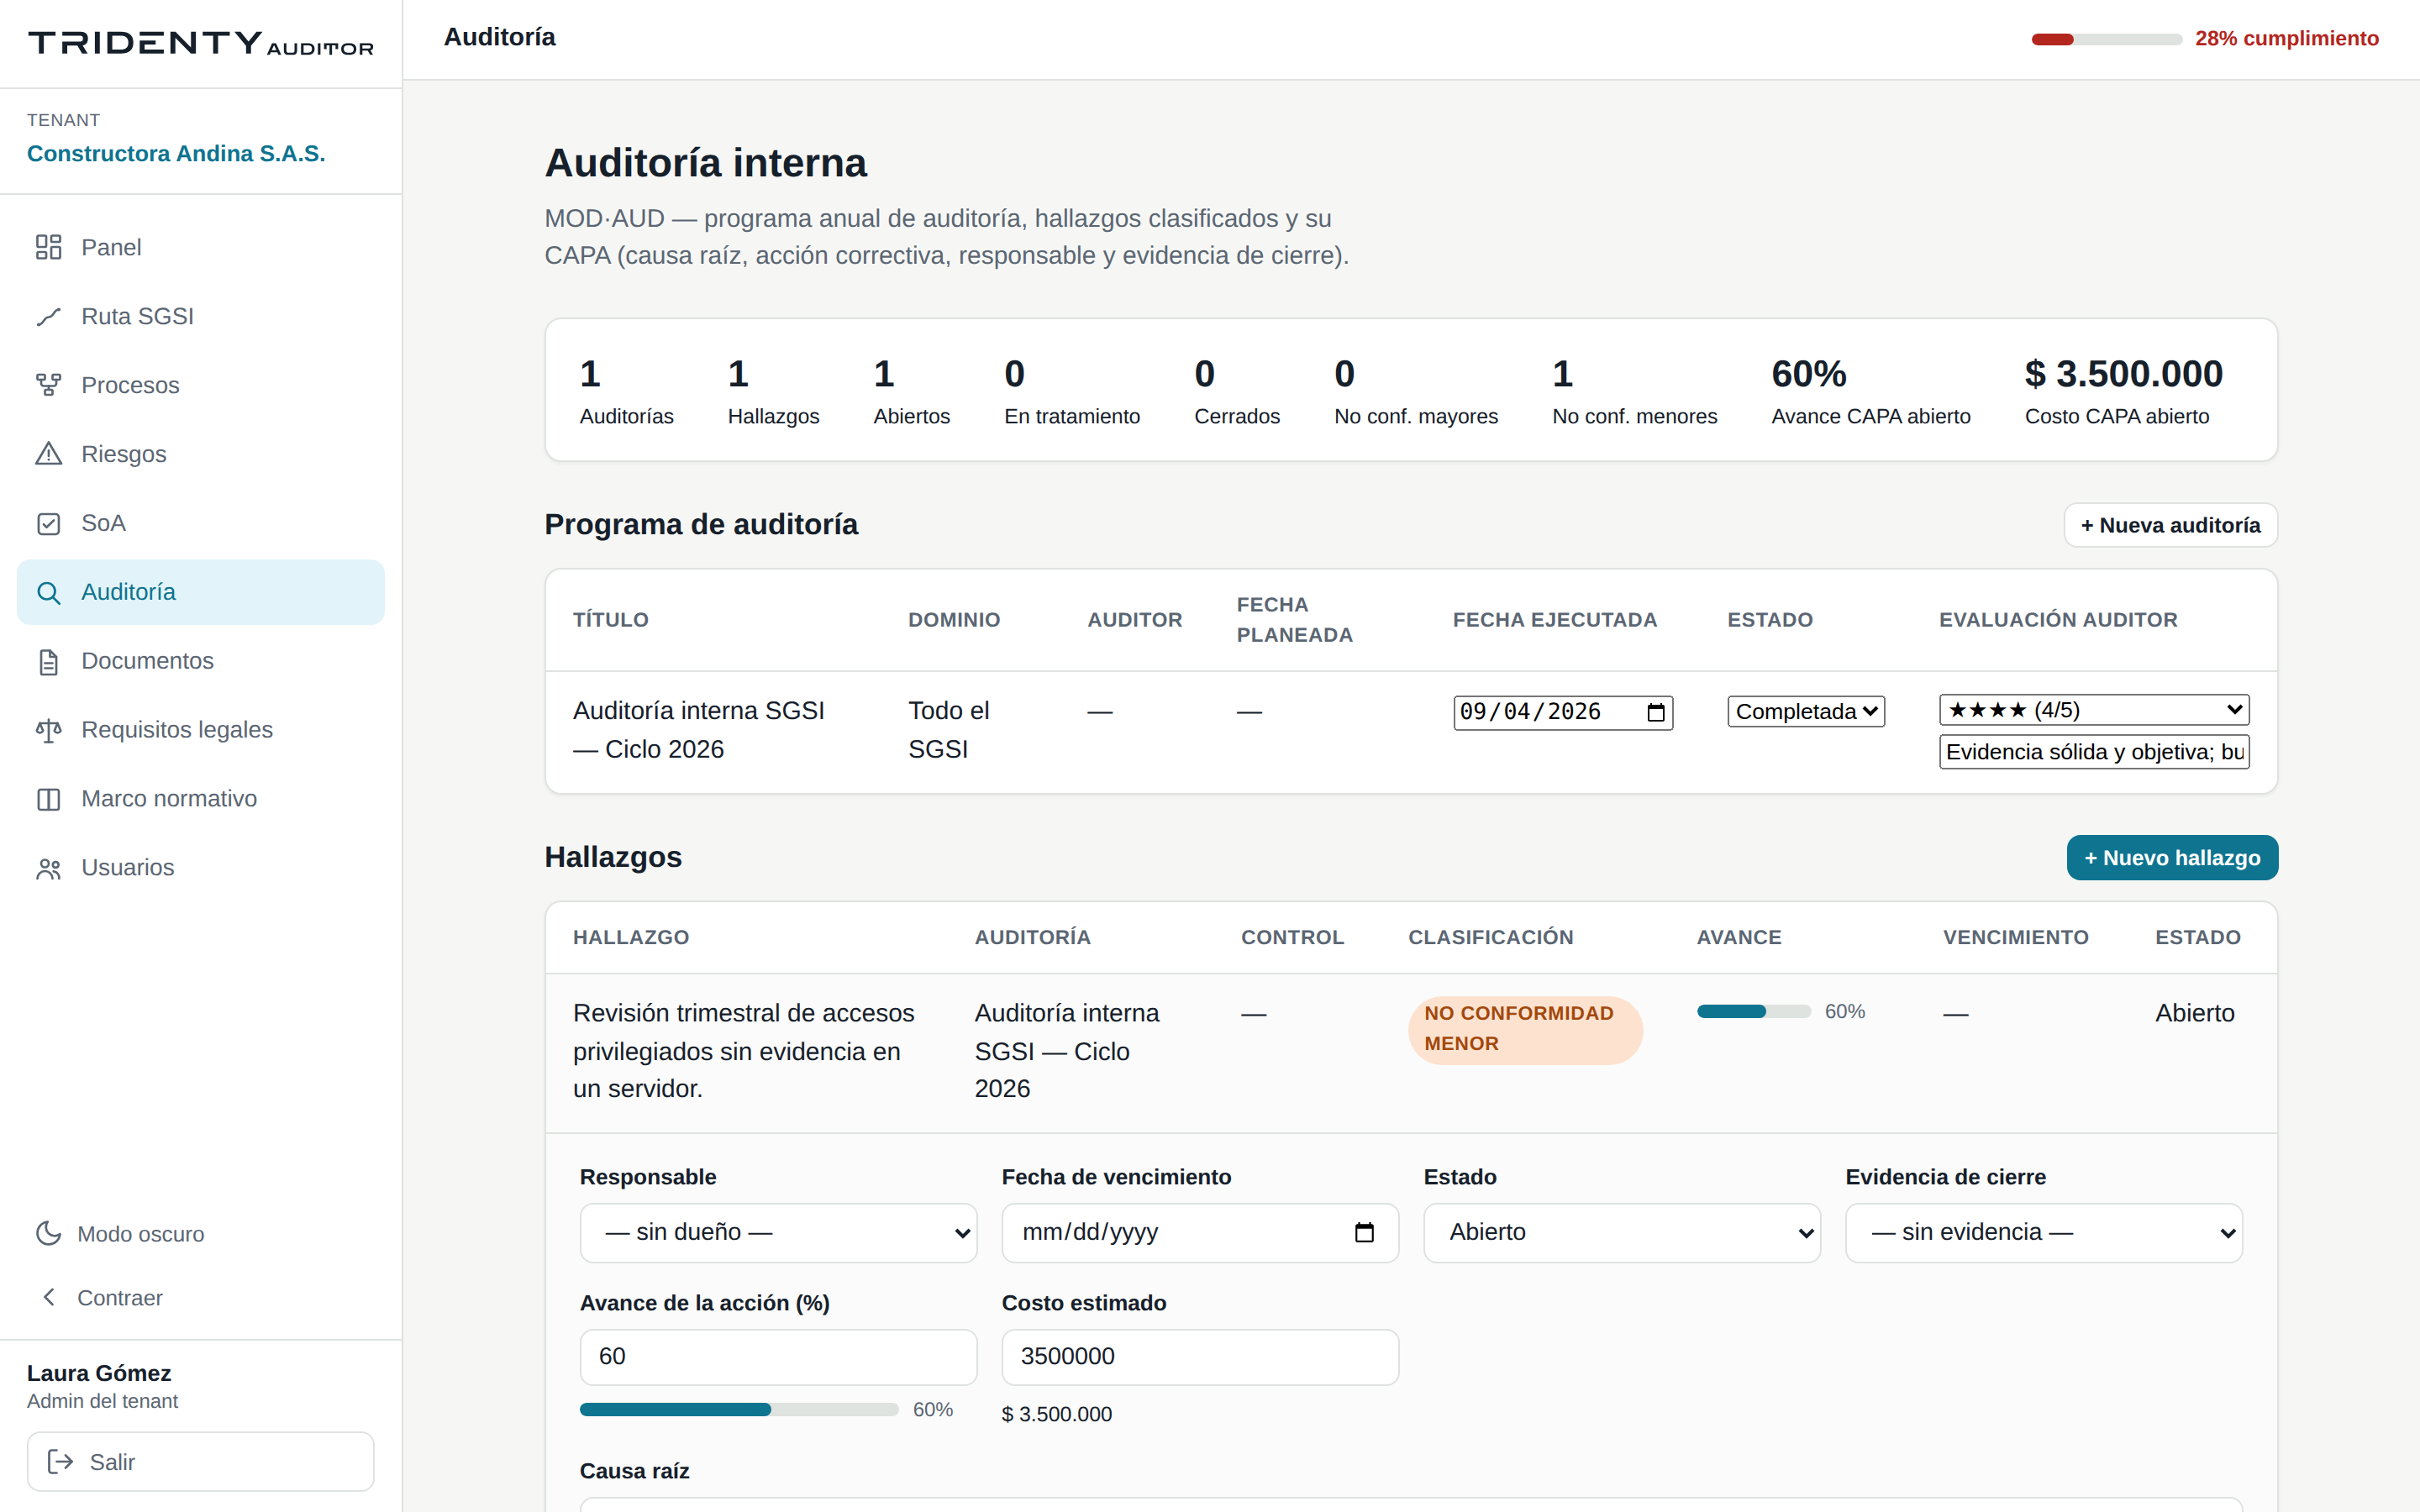
Program with auditor assessment, classified findings and CAPA with % progress and estimated cost.
SUPPORTED STANDARDS
Each tenant chooses its standard on creation, so incompatible structures are never mixed.
93 controls · 4 domains · 8-phase Path
The international information security management standard, with its full Annex A.
41 controls · 10 sections · 58 requirements · 10-phase Path
The regulatory requirement of Colombia's National Operation Council (CNO) for power sector agents, with mandatory audits starting in 2026.
The compliance engine behind both is designed to add new standards (NIST CSF 2.0 is on the roadmap) without rebuilding the platform.
A single plan with every module included. Choose the billing cycle that best fits your operation.
Equivalent to USD 125/month: pay for 10 months, get 12.
Request a demoMain option: cloud SaaS. On-premise deployment is evaluated case by case for customers with regulatory or isolation requirements, with the same licensing.
GETTING STARTED
A 45-minute walkthrough on the standard that applies to your organization: ISMS Path or CNO Path, document control with seal and integrity, internal audit.
SaaS tenant ready the same day, with the 134 controls and paths preloaded. In special cases, on-premise container install in under 20 minutes.
Support to load your existing documentation, define processes, owners and responsibilities, and start the path from your real state.
Password recovery and email invitations · second authentication factor (authenticator app) · information asset inventory with a power-sector catalog · internal audit with a standard-derived checklist and sealed report · incident log in the CNO Agreement 2088 format.
Management review with generated minutes · training and competence · security objectives and indicators · NIST CSF 2.0 on the same engine · federated enterprise SSO with the customer's directory · isolated tier for regulated customers.
FAQ
Tridenty Auditor is a GRC platform to implement and audit ISO/IEC 27001:2022 and the CNO Cybersecurity Guide (Agreement 1960). It centralizes documents, risks, the Statement of Applicability, legal requirements and internal audit on the same controls and the same evidence.
ISO/IEC 27001:2022 (93 Annex A controls, 8-phase path) and the CNO Cybersecurity Guide, Agreement 1960 (41 controls, 10 sections, 58 requirements, 10-phase path). Each tenant picks one standard. NIST CSF 2.0 is on the roadmap.
It is the regulatory requirement of Colombia's National Operation Council (CNO) for power sector agents, with mandatory audits from 2026.
Every approved document carries two signatures (reviewed and approved), a SHA-256 hash per version and a stamped PDF as a controlled copy. One click recomputes the hash and confirms nobody altered the file.
The main deployment is cloud SaaS. In special cases, for regulatory or network isolation reasons, it is installed on-premise in containers in the customer's data center, with the same licensing.
A single plan with every module: USD 150 per month or USD 1,500 per year (USD 125/month).
Book a 45-minute guided demo on the standard that applies to your organization and start a pilot the same day.
SaaS · On-premise in special cases · Spanish-language support